Top Security Standards
At IC System, your account inventory and data remain secure through our compliance with the industry’s top security standards. We protect your data, and the data of your consumers, with our ironclad security network and highly regimented compliance protocols. All security measures are tested by more than 50 annual audits and monitored 24/7/365. Below you will find many of the top security certifications and practices that IC System uses to keep our clients’ information safe and secure.
SOC 1 and SOC 2 Type 2 Certified with HITRUST Mapping
IC System holds a SOC 2 Type 2 and SOC 1 Type 2 Certification. Our infrastructure’s hardware, software, personnel, and data handling procedures meet the security standards of the Service Organization Control (SOC) 2 Type 2 and SOC 1 Type 2 audits. Using the latest technology and highest quality solutions, we have the organizational and systemic safeguards in place to protect your consumers’ data.
Developed by the American Institute of CPAs (AICPA), SOC 2 defines criteria for managing customer data (process and controls) based on five “trust service categories”—security, availability, processing integrity, confidentiality, and privacy.
SOC 2 certification is issued by outside auditors. They assess the extent to which a vendor like IC System complies with one or more of the five trust principles based on the systems and processes in place.
S2Score
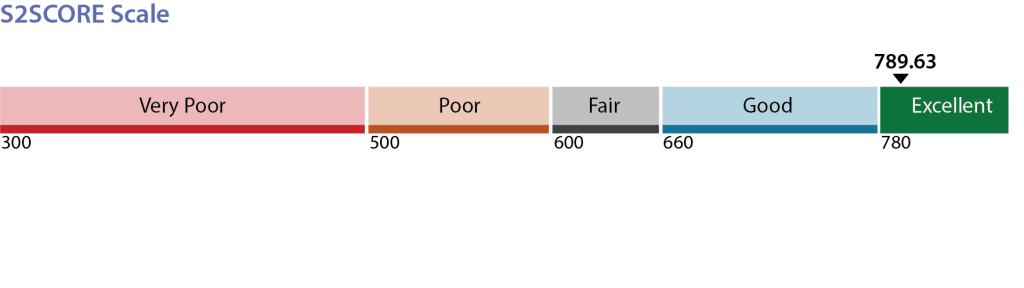
IC System underwent an organizational information security risk assessment by SecurityStudio’s S2ORG service. The results show an overall S2Org Score of 789.63, is well above the industry average. Possible scores range from 300-850.
SecurityStudio, creators of the S2SCORE (formerly FISAScore), provides companies with an easy way to assess their security posture. This gives companies like IC System the chance to better manage and convey their security stance. Their scoring service gives organizations the opportunity to measure the current state of their security, compare their status to other security projects, and identify vulnerabilities that may require attention.
PCI DSS 4.0.1 Annual Certification
Many collection agencies conduct the Payment Card Industry (PCI) Data Security Standard (DSS) self-assessment. IC System completed the more stringent and externally audited, PCI DSS 4.0.1 Report on Compliance (RoC). This audit was performed on the Card Data Environment (CDE). IC System is a Level 1 Service Provider, meaning we process, store, and transmit consumer data in the CDE securely.
Veracode Verified Consumer Pages
IC System’s Consumer Payment Portal and Consumer Self Service Portal have been Vericode Verified. We protect sensitive consumer data with web pages that use highly secure code. Vericode verifies the secure development process around these applications.
The Veracode Verified Standard represents that the following application security practices are embedded into the software development process to ensure consumer data is protected:
- Assessment of first-party code using static analysis
- Documentation that the application does not allow Very High flaws in its first-party code
- Developer access to remediation guidance Verified Standard is the first of three (3) tiers representing the Verified program
ICE™ – IC System’s Intelligent Collection Engine
Our innovative proprietary software, ICE™ (Intelligent Collections Engine) is designed, developed, and maintained at our St. Paul, MN. ICE™ incorporates industry rich features capturing every dimension of the receivable management business. ICE™ incorporates the experience and knowledge gained over our eight decades in the collections industry.
ICE™ was developed for maximum productivity and compliance, complete customization capabilities, and unmatched data/analytic functions. Moreover, the ICE™ system also has extensive reporting capabilities, with over 50 standard reports available today and the ability to develop custom reports required.
ISO 27002
IC System is certified for over 100 security and compliance management controls set forth by the International Organization for Standardization. The ISO 27002 offers recommendations and best practices on information security and data management to ensure confidentiality, integrity, and availability of information.
HIPAA/HITECH
IC System is audited for compliance with the Health Insurance Portability & Accountability Act (HIPAA) and Health Information Technology for Economic and Clinical Health (HITECH) Act. HIPAA and HITECH establish security provisions, safeguarding rules, and confidentiality concerns regarding the transmission, use, and storage of healthcare information.
Women-Owned Business Enterprise Certified
The Supplier Clearinghouse for the Utility Supplier Diversity Program of the California Public Utilities Commission has certified IC System as a Women-Owned Business Enterprise (WBE). Companies certified by the Supplier Clearinghouse as women-owned must demonstrate they are at least 51% owned by one or more women and that women are influential in the company’s management and daily operations. The California Public Utilities Commission audits and verifies the status of WBEs while establishing and maintaining a directory of certified vendors. The Clearinghouse audit and verification program precludes the need for our business partners to conduct additional audits to verify IC System’s commitment to workplace diversity.
GLBA Safeguards Rule
IC System is compliant with the Gramm-Leach-Bliley Act (GLBA), or Financial Services Modernization Act of 1996, and certified to collect and store consumer data with security and confidentiality. The GLBA is a federal law that governs how financial institutions handle the private information of consumers. The GLBA regulates third-party collection agencies to:
- Ensure the security and confidentiality of customer records and information
- Protect against any anticipated threats or hazards to the security or integrity of such records
- Protect against unauthorized access to or use of such records or information which could result
Federal Trade Commission’s Red Flags Rule
IC System has implemented an Identity Theft Prevention Program to adhere to the Federal Trade Commission (FTC) Red Flags Rule (“Red Flags Rule”). The Red Flags Rule requires businesses to implement an Identity Theft Prevention Program designed to identify warning signs (e.g. red flags) of identity theft in their procedures. Our company’s Identity Theft Prevention Program is regularly audited for compliance.
Have A Question?
Contact our team to get in touch with a friendly IC System representative.
Get In TouchCollection Agency Data Security and Compliance FAQs
What is SOC 2 and why does it matter for a collection agency?
SOC 2 is an independent examination of a service organization’s controls using criteria established by the American Institute of Certified Public Accountants. A SOC 2 Type 2 report evaluates whether the controls examined operated effectively over a defined period, giving clients evidence about how the organization protects information.
For a collection agency handling sensitive account information, that independent review helps clients evaluate data security before sharing records. IC System undergoes SOC 2 Type 2 audits as part of its security program. When evaluating an agency, review the report’s scope, reporting period, and findings rather than relying on a security logo alone.
What is PCI DSS compliance in debt collection?
PCI DSS stands for the Payment Card Industry Data Security Standard. It establishes technical and operational requirements for protecting payment card information. In debt collection, it applies to agencies that store, process, or transmit cardholder data, or that could affect the security of the cardholder data environment.
For businesses choosing a collection partner, PCI DSS compliance is an important consideration when the agency accepts card payments from consumers. IC System completes an externally audited PCI DSS assessment of its cardholder data environment, rather than relying solely on a self-assessment.
What security certifications should I require from an agency?
Look for current, independently assessed security documentation that covers the services your organization will use. Request a recent SOC 2 Type 2 report and, when payment card data is involved, a PCI DSS Attestation of Compliance. Have your security team review the assessment dates, scope, and findings. SOC 2 is an audit report, so asking for the underlying documentation is more useful than asking whether an agency is “certified.”
Healthcare organizations should also review the agency’s HIPAA safeguards and establish an appropriate business associate agreement before sharing protected health information when required.
How does an agency protect client data from breaches?
A collection agency should protect client data through restricted access, encryption, multifactor authentication, employee training, and regular security testing. It should also monitor for threats, oversee service providers, and maintain a documented incident response plan. These safeguards help prevent unauthorized access and prepare the agency to respond when a security issue occurs.
IC System supports its security program with independent audits and round-the-clock monitoring. Businesses should ask prospective agencies how they identify vulnerabilities, correct problems, and communicate about incidents. Security practices reduce risk, but no audit or certification guarantees that a breach cannot occur.